A short note on long-lived keys and forgotten service accounts, plus a half-hour review you can do this week.
Short one this time.
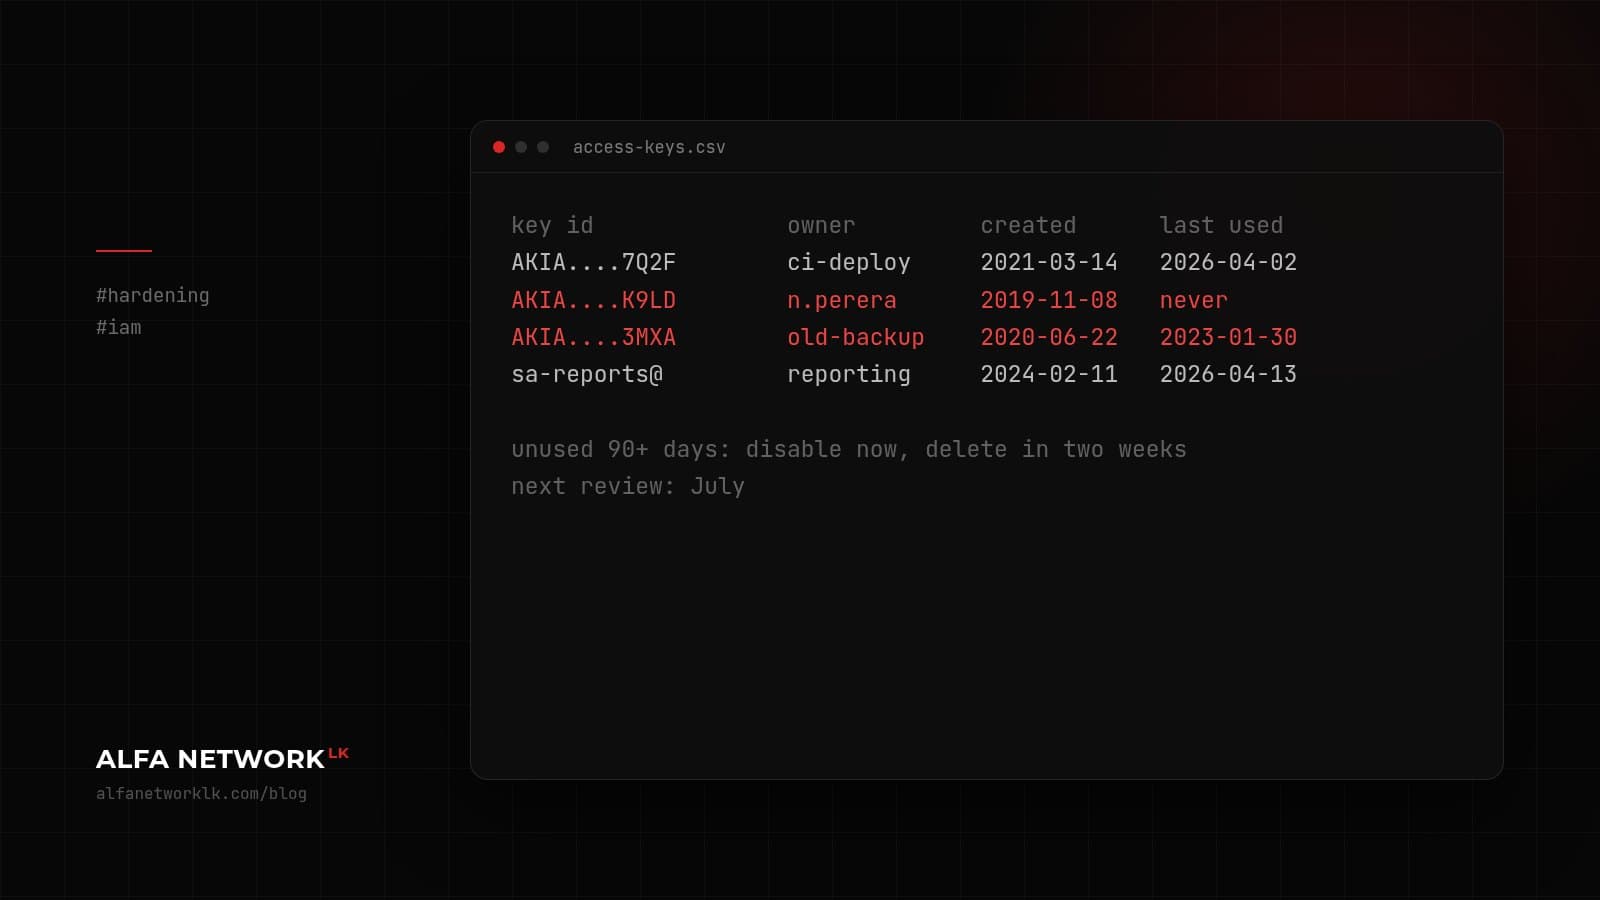
A pattern we keep running into on cloud reviews: an access key created years ago by a developer who has since left, still active, with far more permission than whatever it's used for. Sometimes nobody knows what it's used for at all. Sometimes it's sitting in a CI pipeline, or in a Git repo that turned out to be public.
A review you can do in about half an hour, whichever cloud you're on:
- List every access key and service account with its last-used date.
- Anything unused for 90 days, disable it (don't delete yet). If nothing breaks in two weeks, delete it.
- Anything with admin or owner rights, ask who needs that and write down the answer.
- Check the break-glass admin account has MFA, and that its password isn't saved in someone's browser.
Where the platform supports it, move CI jobs and workloads to short-lived credentials (IAM roles on AWS, workload identity federation on GCP, managed identities on Azure) so there's no long-lived key to leak in the first place.
Then set a calendar reminder to do it again in three months. That part matters more than it sounds.
Comments (0)
No public comments yet.