You don't need a zero trust 'platform'. You need to stop treating the office network as safe, and you can start with what you already pay for.
Every few weeks someone forwards us a vendor deck with "zero trust" on every slide. The idea behind it is good and fairly simple: being on the office network, or on the VPN, shouldn't be enough to reach everything. Each login and each connection gets checked on its own merits.
The problem is that the marketing makes it sound like a project for a bank with a big security team. Most of the companies we talk to have one IT person, sometimes two, looking after a head office, a few branches, and people working from home when the traffic is bad.
For that kind of setup, this is roughly where we'd start.
First, get everyone onto one identity. If you're on Microsoft 365 or Google Workspace, that's already your identity provider. Turn on MFA for everyone, not only managers, and use an authenticator app instead of SMS where you can. Then get rid of the shared accounts: the accounts@ mailbox that four people log into with one password, the "admin" login on the firewall that everyone knows.
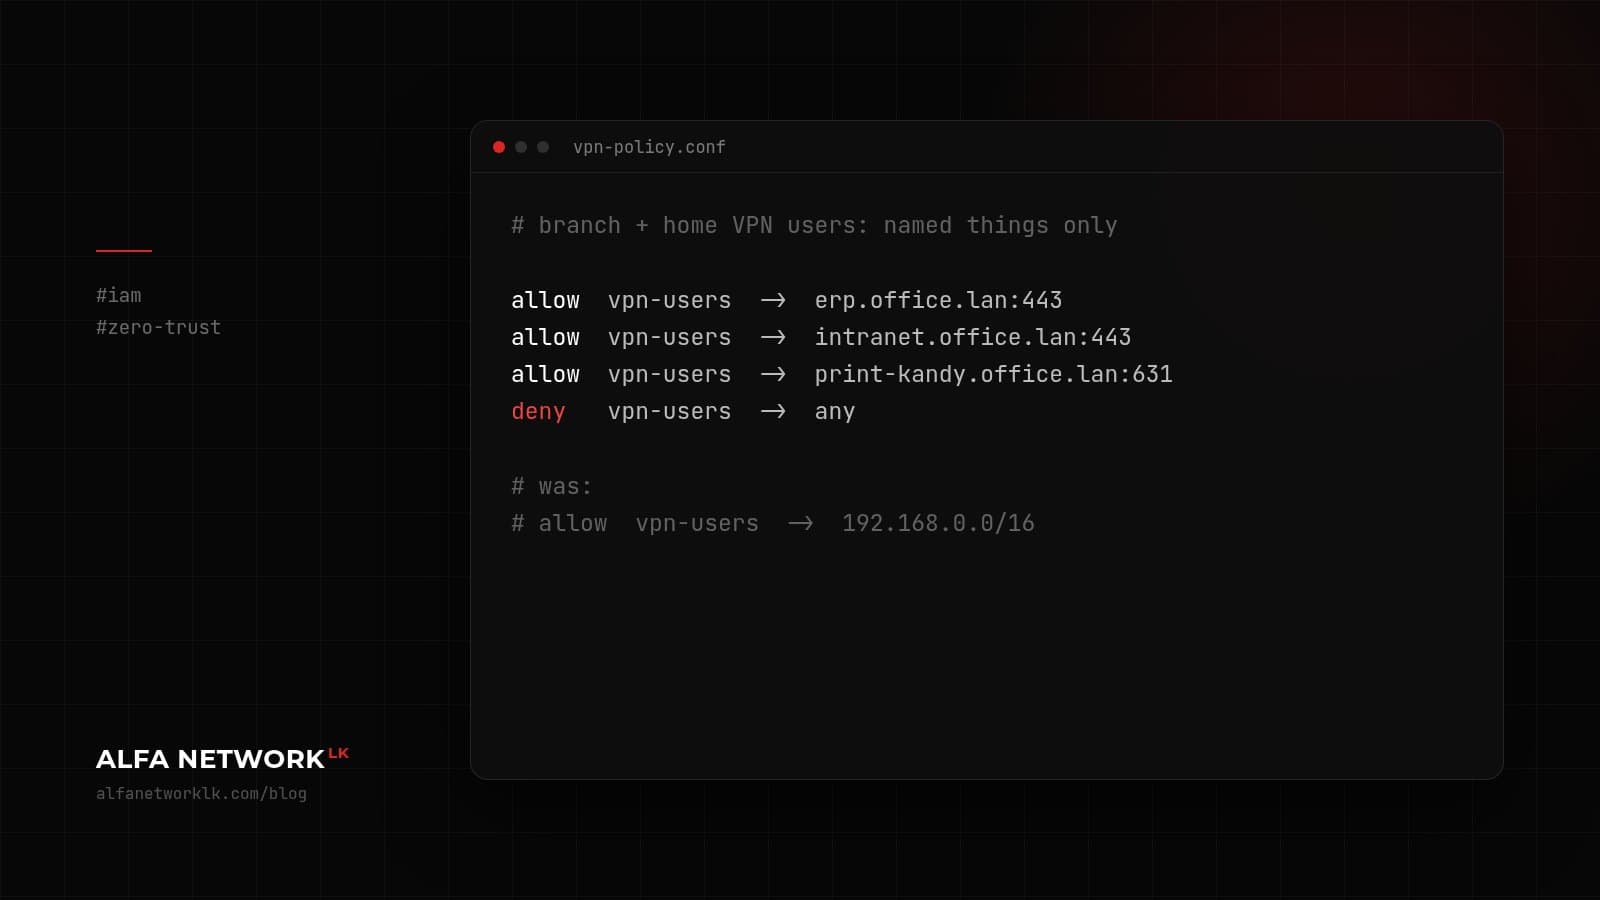
Second, stop letting the VPN mean full access. A lot of branch setups we see drop VPN users onto the same flat network as the servers. If one laptop picks up malware at home, it now has a direct line to the file server and the accounting database. Even basic firewall rules that say "VPN users can reach these three things and nothing else" make a real difference.
Third, look at the laptops. You don't need perfect device posture checks on day one. Knowing which laptops exist, that disk encryption is on, and that they're getting updates is already more than many companies can say. If you're licensed for Intune or Google's endpoint management, it can enforce most of this.
After that it's gradual. Move one app at a time behind proper sign-in. Keep a record of who signed in from where. Remove access on the day people leave (this one is always worse than people think).
If a vendor tells you zero trust starts with buying their product, ask them what you should do with the licences you already have. A good one will have an answer.
Comments (0)
No public comments yet.